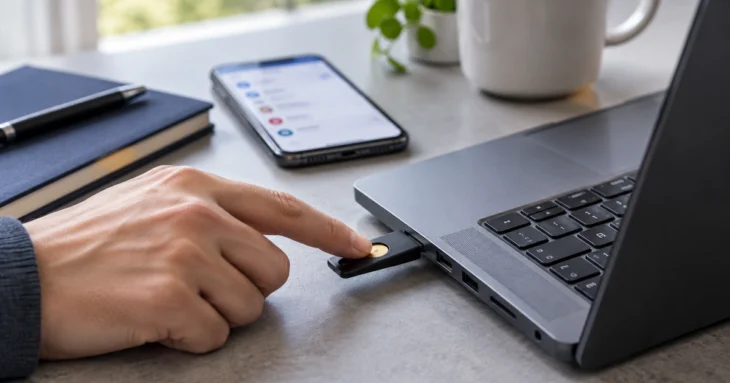
Password advice has changed. Long, unique passwords are still important where passwords remain, but businesses now have practical options that reduce how often employees need to type a password at all.
Passkeys are especially important because they are designed to resist phishing: the credential is tied to the legitimate service rather than being a secret a user can accidentally type into a fake website. Microsoft is actively moving Entra environments toward passkeys, which makes this a good time to plan instead of waiting for a forced migration.
What to focus on first
Use a business password manager for remaining passwords
Employees should not be expected to memorize dozens of unique credentials. A managed vault makes strong, unique passwords practical and gives the organization a safer way to handle shared access when sharing is unavoidable.
Use a strong passphrase for the vault
The password-manager master credential should be long, unique, and memorable. It is one of the few secrets an employee may still need to know directly.
Start passkeys with high-risk users
Administrators, finance staff, executives, and people with broad cloud access are good early candidates. They face higher consequences from successful phishing and are usually a manageable pilot group.
Plan recovery before rollout
Decide how users regain access after losing a phone or security key, and how the help desk verifies identity. Weak recovery procedures can undermine strong authentication.
Keep MFA during the transition
Moving toward passwordless does not mean turning off protection prematurely. Maintain strong authentication policies until the new method is enrolled, tested, and supported across the applications employees actually use.
Common ways this goes wrong
- Using browser-saved passwords as the company’s only credential-management strategy.
- Rolling out security keys without spare-key and account-recovery procedures.
- Assuming every SaaS application supports the same passkey or SSO experience; inventory compatibility first.
Make it part of normal operations
Treat this as a recurring operating responsibility, not a one-time project. Review the control after major account, application, network, or staffing changes; keep ownership clear; and make sure important exceptions are written down. A small business does not need a complicated governance program, but it does need to know who notices when a protection stops working and who has authority to fix it.
Questions worth bringing to your next IT review
- Can we explain how the ‘Use a business password manager for remaining passwords’ practice works today without relying on one person’s memory?
- Where do we have exceptions to ‘Use a strong passphrase for the vault’, and are those exceptions still necessary?
- Who owns the work behind ‘Start passkeys with high-risk users’, and what evidence shows it is working?
- How would we discover that this control or process stopped working?
- What business, staffing, vendor, or technology change should trigger another review?
What a solid approach looks like
The destination is not “no passwords tomorrow.” It is fewer reusable secrets, stronger authentication for important systems, and a recovery process that does not create a weaker back door. A phased rollout is usually easier for employees and IT alike.
If you want to go one level deeper, see MFA Fatigue Attacks.
If your organization would benefit from help reviewing the current environment or turning these ideas into a workable plan, IT Consulting from CTResources is available as a practical next step. The goal is to strengthen what matters without adding unnecessary complexity.