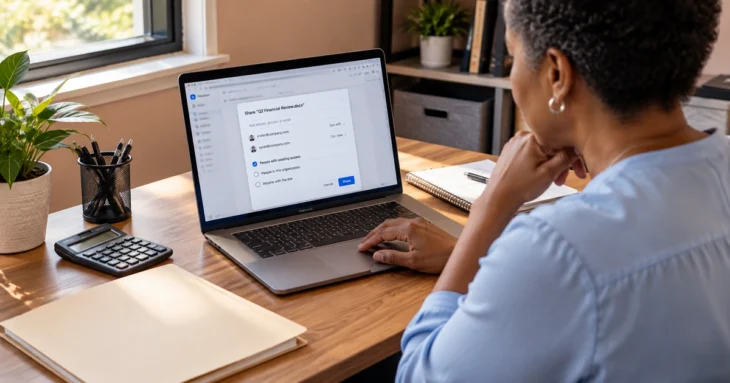
Not every data leak starts with an attacker. A public sharing link, an email sent to the wrong contact, or a former employee who still has access can expose information just as effectively.
Cloud collaboration makes work faster because sharing is easy. The security challenge is keeping “easy” from becoming “uncontrolled.” Small businesses can reduce accidental exposure without locking every folder down by using sensible defaults, data classification, and a review process for external access.
What to focus on first
Tighten default sharing settings
Make “specific people” or authenticated access the normal option for sensitive content. Public or anonymous links should be the exception, not the easiest button.
Know where sensitive data lives
Identify locations that contain customer records, payroll, HR data, contracts, financial information, or other restricted material. Apply stronger controls there instead of treating every file identically.
Use DLP and policy tips carefully
Where licensing supports it, use data-loss-prevention rules to warn or block risky sharing of recognizable sensitive data. Start in audit or warning mode so the policy can be tuned without disrupting legitimate work.
Review guests and external links
External collaboration often outlives the project that created it. Schedule reviews of guest accounts, shared folders, and anonymous links, especially in departments that work with many vendors or clients.
Build offboarding into access cleanup
Removing the employee account is only part of the job. Transfer file ownership, revoke shared links where needed, remove external app connections, and review delegated mailbox or drive access.
Common ways this goes wrong
- Using “anyone with the link” because it is convenient for one project and leaving it in place forever.
- Assuming cloud-provider security controls automatically understand which information your business considers sensitive.
- Deploying strict DLP rules all at once without testing how normal workflows behave.
Make it part of normal operations
Data protection works best when the safe choice is also the easy choice. Set defaults around sharing, storage, and approved tools, then review the higher-risk locations on a schedule. When employees need an exception, give them a fast path to ask rather than encouraging workarounds. The business should know where its most sensitive information lives and who can grant access to it.
Questions worth bringing to your next IT review
- Can we explain how the ‘Tighten default sharing settings’ practice works today without relying on one person’s memory?
- Where do we have exceptions to ‘Know where sensitive data lives’, and are those exceptions still necessary?
- Who owns the work behind ‘Use DLP and policy tips carefully’, and what evidence shows it is working?
- How would we discover that this control or process stopped working?
- What business, staffing, vendor, or technology change should trigger another review?
What a solid approach looks like
The goal is not to prevent collaboration. It is to make the safe sharing path the normal path and to give the organization enough visibility to find exceptions. Thoughtful defaults often reduce more risk than a long list of rules employees try to work around.
If you want to go one level deeper, see Cloud Security Basics.
If your organization would benefit from help reviewing the current environment or turning these ideas into a workable plan, IT Consulting from CTResources is available as a practical next step. The goal is to strengthen what matters without adding unnecessary complexity.